CRITICAL PHP SECURITY ALERT:
PHP2SHELL (CVE-2026-109618 & 109619)
Two critical vulnerabilities allow unauthenticated attackers to execute arbitrary system code on internet-facing PHP deployments. Even if your website appears completely normal on the frontend, your server may already be silently compromised.
Watch The Security Explainer
A visual breakdown of the PHP vulnerability, why unauthenticated remote code execution is severe, and what website owners must verify immediately.
Why Unauthenticated RCE Is The Highest Category Threat
Remote Code Execution (RCE) with a CVSS score of 9.2 means an attacker located anywhere in the world can run arbitrary commands on your web hosting environment without needing any login username or password.
How The Exploit Works
The vulnerability lies in how specific internet-facing PHP CGI and FastCGI module configurations handle query strings and request parameters. When an attacker sends crafted request inputs, the PHP engine misinterprets options, allowing the attacker to inject arbitrary commands into the host operating system.
Crafted Query Argument -> Handler Argument Injection -> Unauthenticated OS Command ExecutionOnce a shell is opened, attackers can read database passwords, dump user tables, install crypto miners, or lock your files with ransomware.
Who Is Vulnerable?
- WordPress Websites: Running on standard cPanel, Apache, LiteSpeed, or Nginx with unpatched PHP runtimes.
- Custom PHP Applications: CRMs, booking portals, and inventory tools built on legacy PHP versions.
- Unmanaged Cloud VPS / Dedicated Servers: Systems where server packages have not been upgraded to the latest point releases.
Everything You Need To Know At A Glance
Switch between the English and Hindi advisory creatives below. Share these with your technical team or developer immediately.
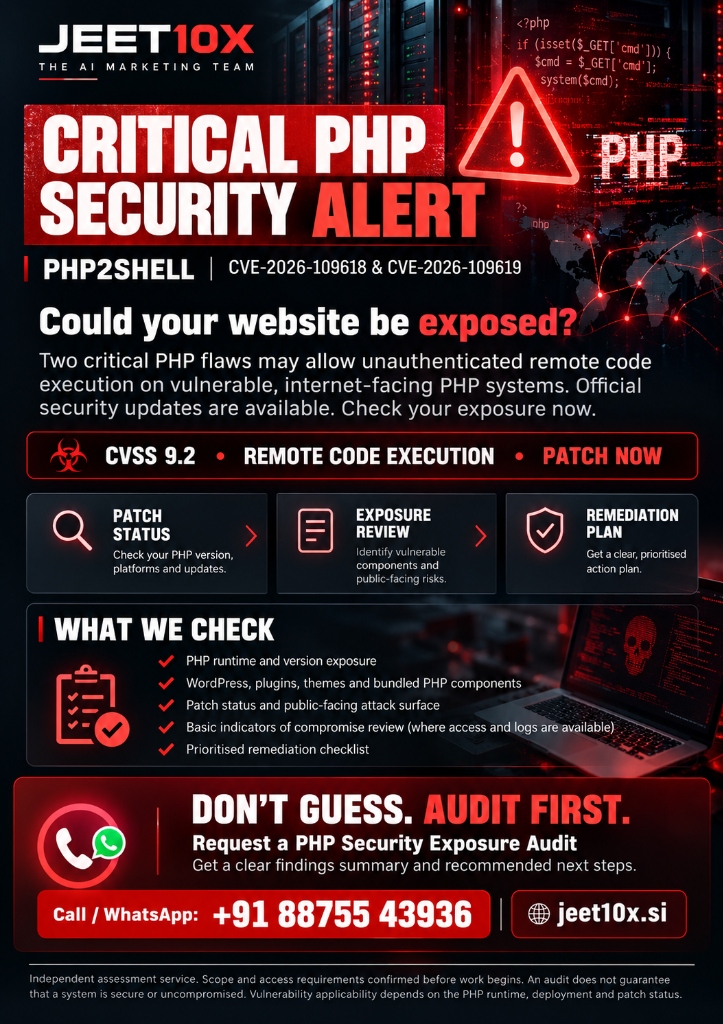
Our 3-Point Rapid Security Audit
We diagnose your live environment without causing downtime or disrupting customer operations.
Runtime & CGI Exposure Check
We inspect your host server handler (mod_php, php-fpm, cgi-fcgi), active runtime version, and verify if the specific attack arguments can be intercepted or executed.
Web Server & WAF Hardening
If immediate runtime patching is not provided by your hosting provider, we implement rewrite-level blocking rules at Nginx, Apache, or Cloudflare level to immediately deflect exploits.
Persistence & Backdoor Scan
We perform an integrity verification of core CMS files, upload folders, and cron tasks to ensure no unauthorized web shells or persistence hooks were dropped prior to patching.
What You Receive In Your Audit Report:
Request Your Emergency PHP Security Audit
Fill in your details below. Our technical team will review your domain and coordinate the audit protocol within 24 hours.
Official Public Service Advisory by JEET10X. All audits are executed under strict non-disclosure agreements.